Continuous Threat Monitoring
Designed to analyze telemetry for suspicious patterns and surface events requiring attention.
THE NEXT EVOLUTION OF SECURITY OVERSIGHT
Hyper-Intelligent Cyber Defense Platform. Executive-level visibility, threat intelligence and cybersecurity advisory.
 X-50Up to 50
 X-10050–100
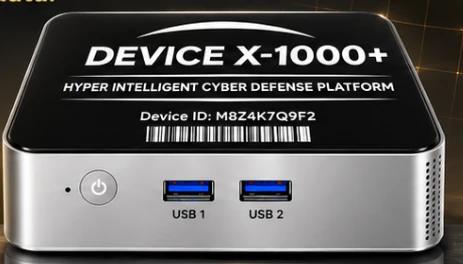 X-1000+1,000–2,000
PRIVATE CONSULTATION
Tell us about your environment. We'll discuss security requirements, device coverage, deployment fit and the appropriate DEVICE X configuration.
CAPABILITIES FOR MODERN INFRASTRUCTURE
Cyber intelligence that informs business decisions—not another screen full of unactionable noise.
Designed to analyze telemetry for suspicious patterns and surface events requiring attention.
Prioritized notifications for indicators of compromise, operational risk and abnormal activity.
Inventory and device insight based on available network sensors and authorized integrations.
Analyze supported traffic patterns, DNS activity and connection behavior for anomalies.
Consolidate security signals, trends and remediation priorities into decision-ready reports.
Security architecture consultation, guided triage and practical next-step recommendations.
Product functions and integrations shown are planned solution capabilities and must be confirmed during scoping. Monitoring availability does not imply continuously staffed analyst services or automated attack prevention.
INTELLIGENCE WITH EXECUTIVE CONTEXT
Device X is designed around an intelligence-led workflow: observe relevant activity, contextualize risk, escalate credible threats, and support informed response decisions.
Visibility and intelligence. Human-directed action.
COMPREHENSIVE RISK CATEGORIES
Visibility, detection and mitigation planning for a broad range of threats—when the necessary sensors, software, integrations and response controls are in scope.
Important coverage distinction: Detection, alerting, blocking, prevention, remediation and 24/7 staffed response are different functions. No standalone appliance protects against every attack. Actual controls and supported threats are established in the project scope and should be validated before contractual commitments.
CHOOSE YOUR ENVIRONMENT
Three premium product configurations, with custom design available for environments outside standard device bands.
SMALL ENVIRONMENTS
Up to 50 devices
For homes, independent professionals and small-business infrastructure needing clear security visibility.
Configuration-based quotation
Request X-50 ConsultationRECOMMENDED FOR GROWTH
GROWING OPERATIONS
50–100 devices
For expanding teams and multi-location organizations with more complex security monitoring needs.
Configuration-based quotation
Request X-100 ConsultationENTERPRISE & MULTI-SITE
1,000–2,000 devices
For complex enterprises and distributed environments requiring tailored architecture and governance.
Custom enterprise quotation
Request Enterprise BriefingWe can discuss a custom deployment architecture, licensing, sensor placement and service model.
A DISCIPLINED SECURITY WORKFLOW
A structured approach from environment assessment through measurable ongoing visibility.
Review network architecture, desired sensors, integrations and security objectives before installation.
Collect approved telemetry and monitor for risk indicators in the configured coverage area.
Assess anomalies and correlate observed activity with relevant security intelligence.
Route findings for authorized response, remediation planning and continuous security improvement.
MORE THAN AN APPLIANCE
Security programs succeed when technology, executive leadership and operational accountability work together.
Security direction informed by decades of enterprise IT leadership and governance experience.
Focus on business exposure, data protection, decision rights and practical defense priorities.
Information translated for business owners, technology executives and operational leadership.
Designed for remote-first discovery and advisory across organizations throughout the United States.
QUESTIONS ANSWERED
The family is proposed for smaller networks through enterprise environments. The appropriate configuration depends on actual device count, throughput, topology, integrations, data sensitivity and support requirements.
No. Cybersecurity is layered. DEVICE X is designed to support security awareness and appropriate defensive controls; it cannot promise prevention of every compromise. Protection depends on architecture, the actual installed software, network placement, integrations and operational response.
Not necessarily. Automated continuous telemetry processing and 24/7 human-staffed SOC monitoring are separate services. Human response coverage and any guaranteed response times must be documented in a service agreement.
Not inherently. A network appliance does not automatically inspect endpoint files, email inboxes, cloud tenants or USB activity. Those capabilities require appropriate additional sensors, endpoint software, email security services or integrations as applicable.
Deployment timing depends on procurement, hardware setup, network architecture, security permissions, integrations and testing. A project-specific implementation schedule is prepared after technical discovery.
No single product guarantees regulatory compliance. American CIO can assist with security controls and readiness reviews, but compliance requires a broader program of administrative, physical and technical safeguards. Legal obligations should be reviewed with qualified counsel.
Yes, custom architectures can be scoped for 101–999 devices, deployments beyond 2,000 devices, multi-location infrastructure or special compliance and security objectives, subject to technical feasibility.
Yes. Complete the consultation form on this page or contact contact@americancio.com. A demonstration will depend on product readiness and scheduling.
YOUR DATA. YOUR BUSINESS. YOUR FUTURE.
Start with an executive-level conversation about your environment, your exposure and your next step toward a stronger cyber defense posture.